Building Hackbot v1: a practical starting point
A practical starting point for building a supervised hackbot for bug bounty research.
A practical starting point for building a supervised hackbot for bug bounty research.
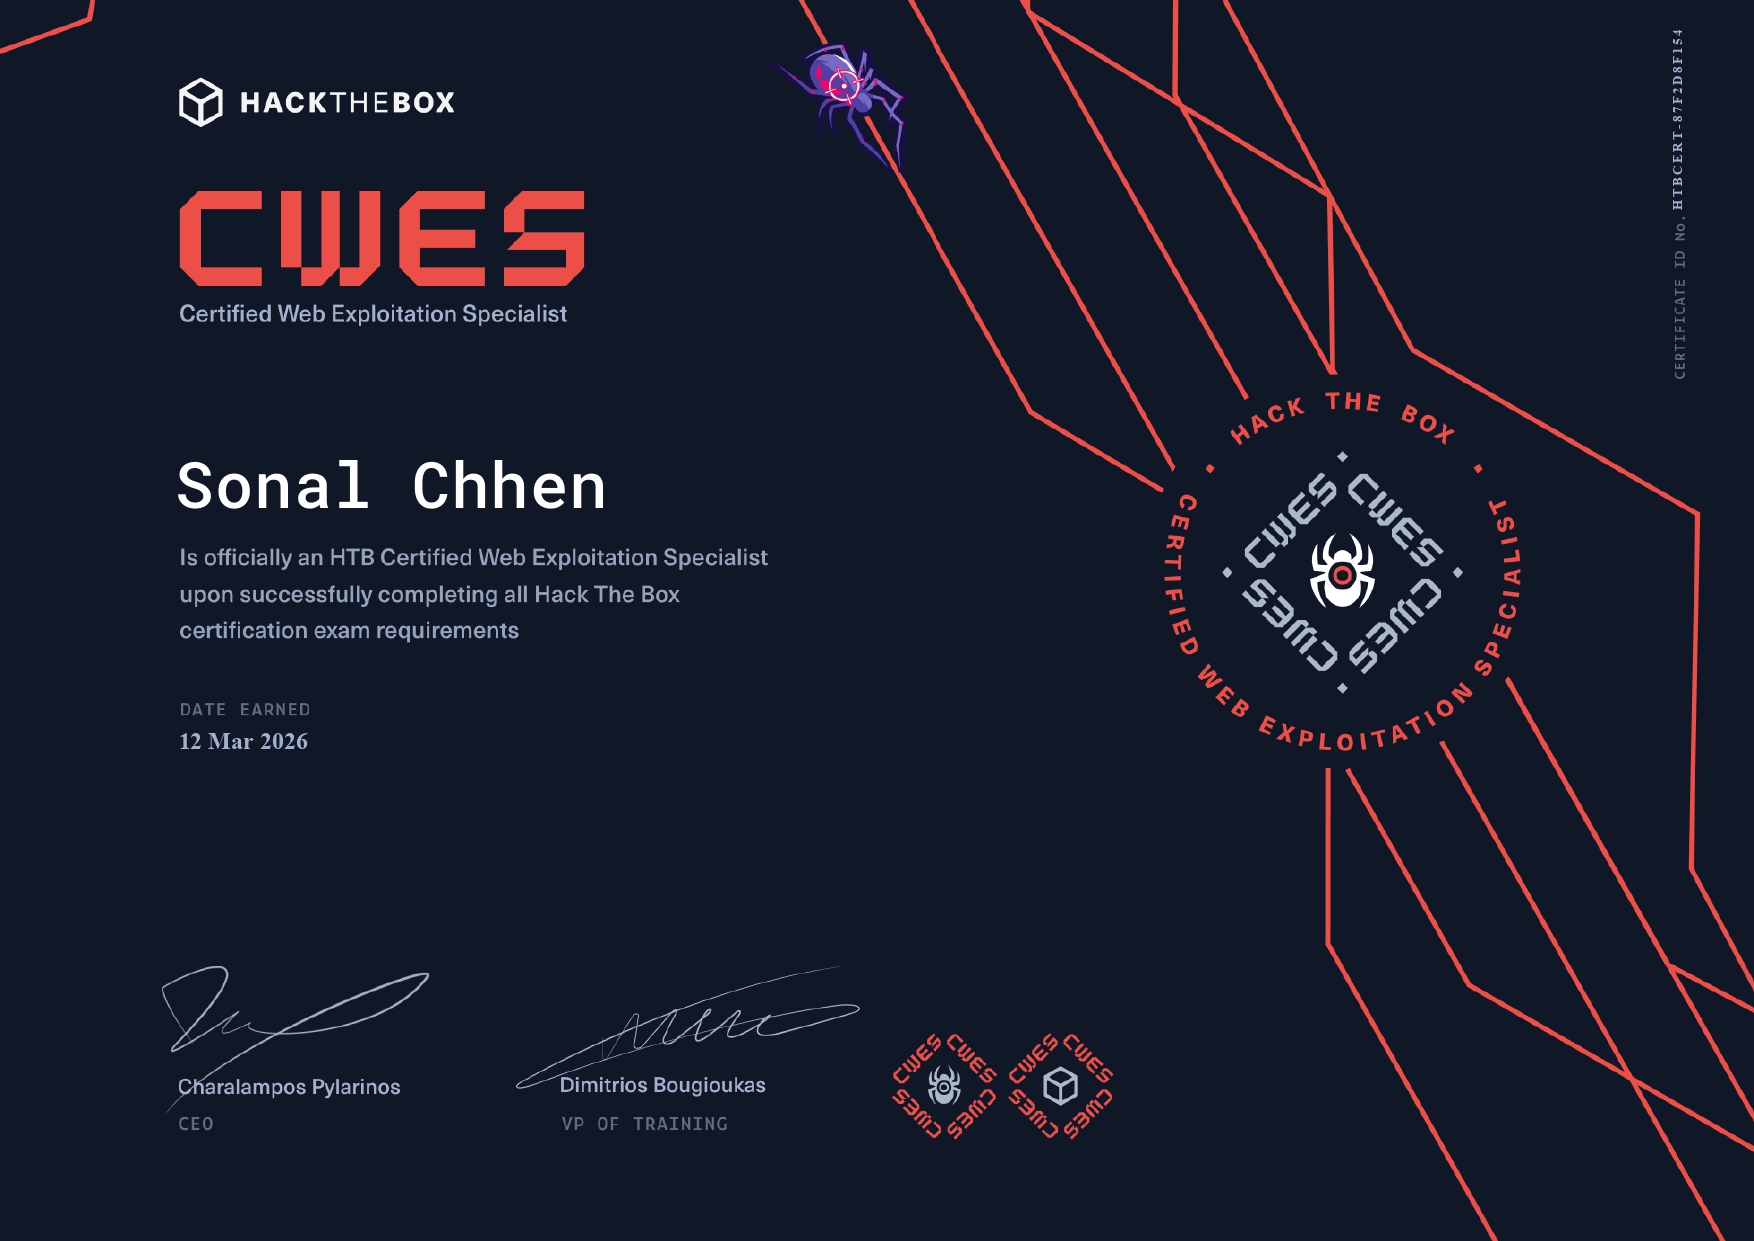
i passed the htb certified web exploitation specialist exam. i spent my holiday break working through the academy modules, taking notes, and practising, then started the exam with a week left befor...
this is my personal cheatsheet collection for the Certified Web Exploitation Specialist (CWES) cert. i’m sharing the structure and tools i used while studying, not to hand you answers, but hopefull...
This post removes the safety refusal from a small open model two different ways and measures the result with several metrics. To follow it you need a rough picture of how these models are trained, ...
Devvortex is an easy Linux box featuring a vulnerable Joomla CMS with an information disclosure vulnerability (CVE-2023-23752) that leaks database credentials. After gaining admin access to Joomla,...
XSS (cross-site scripting) is all about injecting malicious scripts into pages viewed by other users. three main types – stored, reflected, and DOM-based. know when each one applies. additional re...
this section covers HTTP verb tampering, IDOR, and XXE — three classic web attack techniques. different mechanisms, but all very common in real-world apps and CTFs. HTTP Verb Tampering web serv...
sql injection is still one of the most impactful vulnerabilities out there. understand the fundamentals manually first, then let sqlmap do the heavy lifting. SQL injection fundamentals MySQL co...
server-side attacks target the server’s own processing logic. SSRF, SSTI, SSI, and XSLT are all different flavours – each with its own detection and exploitation path. SSRF (Server-Side Request ...
passive recon is all about gathering info without touching the target directly. no packets sent to them, no noise, just public sources and smart googling. the goal is to build a picture of the targ...